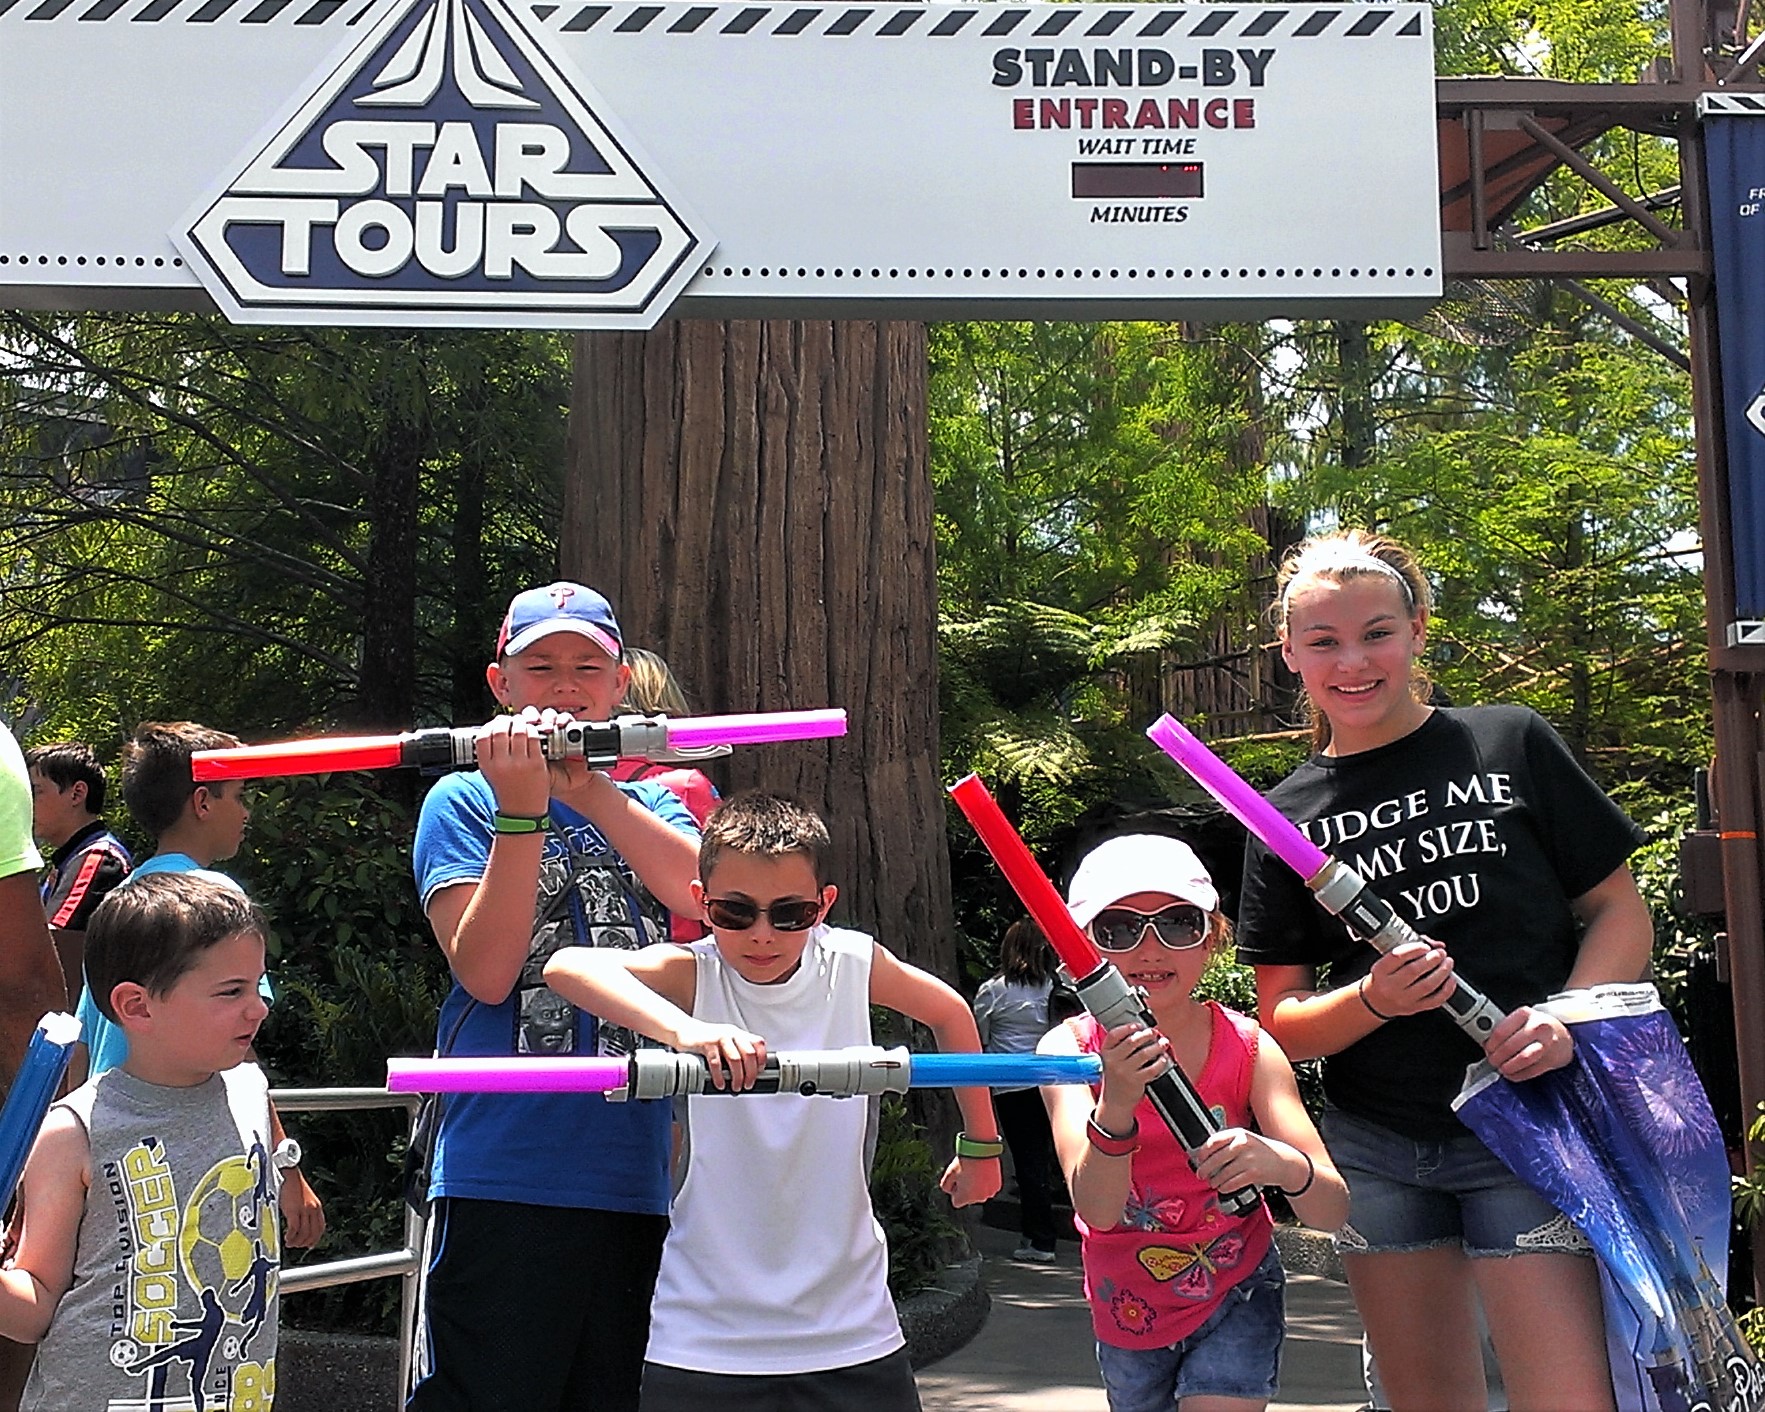
Personalized phishing scams do not always begin with a wild lie. Sometimes they begin with several pieces of truth: a conference you attended, a trip you took, a race your family supported, or a photograph you shared online. After returning from the Momentum Workshop in Florida and traveling to Washington, D.C., to support my son at the Marine Corps Marathon, I began thinking about all the ordinary digital breadcrumbs those trips created.
A scammer would not need a secret file about me. An event name, a location, and the name of someone I trust might be enough to build a message that feels legitimate.
In this episode of Mr. Fred’s Tech Talks, we look at how phishing becomes personal, how artificial intelligence makes targeted messages easier to create, and what families and educators can do without becoming afraid to share anything online.
What You Will Learn
- How ordinary public details can become convincing phishing bait
- The difference between broad phishing and targeted spearphishing
- Why polished design, perfect grammar, and familiar details do not prove a message is real
- How AI can help scammers personalize messages more quickly
- What to do if you already clicked or entered a password
Pause and Verify
The strongest question is not simply, “Does this look real?”
A better question is: “Can I verify this without following the path the message gave me?”
Before clicking a link, opening an attachment, scanning a QR code, or sharing information, ask:
- What is this message asking me to do?
- What pressure is it using to make me act quickly?
- Where can I verify the request independently?
If a bank sends an alert, open the bank’s app yourself. If a social platform sends a password warning, go directly to its security settings. If a friend or coworker makes an unusual request, contact that person through a conversation you already trust.
Build Your Defense Before You Need It
- Use a unique password for every important account
- Use a reputable password manager
- Turn on multifactor authentication
- Use a passkey when a trusted service offers one
- Keep devices and applications updated
- Report suspicious messages when possible
The Breadcrumb Challenge
Look at your last three public posts as if you were trying to create a believable message aimed at you. What could someone learn about an event, location, hobby, workplace, family connection, or person you trust? Imagine one message that could be built from those details. Then decide how you would verify it without using the link, phone number, QR code, or reply button provided in the message.
For a bonus step, improve one security habit:
- Turn on multifactor authentication
- Create a passkey
- Update a reused password
- Review a privacy setting
- Install a waiting security update
Resources
- National Cybersecurity Alliance: Cybersecurity Awareness Month
- AI and the Future of Phishing Interactive Tool
- How to Spot and Avoid Phishing Scams
- How to Create and Remember Strong Passwords
Closing Call to Action
If this episode helped you think differently about your digital breadcrumbs, share it with one person who could use the reminder.